If you've been wanting to do some testing again, then you're in luck - Microsoft has just released Office 2010 SP1 for download. http://www.techspot.com/news/44454-microsoft-releases-office-2010-sp1.html gives some more information and direct download links are below:
http://www.microsoft.com/download/en/details.aspx?id=26622 (x86)
http://www.microsoft.com/download/en/details.aspx?id=26617 (x64)
Thanks to Peter Hale for giving me the heads up on this.
Regards,
The Outspoken Wookie
Wednesday, June 29, 2011


Thursday, June 23, 2011
BPOS Down Again?
OK, so while we're talking about Cloud services with their security and stability issues, Microsoft looks like they wanted to get a mention again, so here we go! BPOS was down again earlier this week - their North American offering was down yesterday (Wednesday) for 3 hours from 11:00AM US Eastern Time - right in the middle of the work day.
The Cloud has promise, sure, but if you can't affort outages where you have no real control over the recovery, sometimes keeping your infrastructure in-house makes a lot more sense. Microsoft seems to have some way to go before they put these network infrastructure issues behind them and can offer a truly redundant cloud solution.
Regards,
The Outspoken Wookie
Online Storage, Syncing & Backup
Up until recently, there was an application that I used and recommended called Dropbox that was used for online storage - you could run the app on multiple computers, your iPhone, iPad, Android or even Blackberry device and sync the data. OK, on mobility devices you won't get the whole size syncing, but you can choose a file and access it once it downloads (sane usage of expensive 3G/HSPA bandwidth).
Then Dropbox went and changed its T&Cs to let the US Government "hands on" department have access to my data if and when they chose. OK, as I don't store anything illegal nor compromising up there, I didn't care. Then they changed things so that any of their employees could access my data, which isn't good. And then, to top things off, they went and released an update that results in open slather access by anyone to anyone's data and that was the straw that broke this camel's back.
Sure, this latest issue was a poor coding, poor internal procedures, poor quality control issue, but it was also a massive security issue following on after Sony, Acer, Sega, Nintendo and other high profile companies had their confidential customer data breached. This chasm has since been closed, however I don't like how easy it was for their internal checks and balances to be utterly defeated by the poor coding skills of one programmer.
Dropbox should have a) known and b) done better.
So, as the major failure of Dropbox is in the security (sic) of your data being applied at their server end, not at your client end, I've looked around for an alternative to Dropbox where I have some control over the security - SpiderOak seems to offer this.
SpiderOak lets you choose whether you want to back data up to the cloud using locally-applied encryption or whether you want to sync a folder on multiple machines that you've signed into using SpiderOak, again using locally-applied encryption - at no point is unencrypted data being stored on the SpiderOak servers. You can also create a "ShareRoom" which allows you to share files with people who you choose, using a "RoomKey" password.
All up, this operates similarly to Dropbox and utilizes real security. Dropbox has dropped the ball in a big way.
Regards,
The Outspoken Wookie
Sunday, June 19, 2011
Outlook: "The name of the security certificate is invalid or does not match the name of the site"
When an SBS 2008 or SBS 2008 R2 (aka SBS 2011) site is configured, sometimes you will find the local (internal) users who use Outlook 2007 or Outlook 2010 (and possibly/probably also Outlook 2003) will receive an error message when first opening Outlook that will report:
Tick - The security certificate is from a trusted certifying authority.
Tick - The security certificate date is valid.
Cross - The name on the security certificate is invalid or does not match the name of the site.
If you press "Proceed", everything runs as normal. This is an annoying message that is caused by some improperly configured Exchange settings (normally caused by initially using a self-signed cert, then later replacing it with a purchased one), all of which are easily rectified after following KB940726, however below I've included the modified instructions for this to apply to an SBS installation.
In the following instructions, "CAS_Server_Name" should be replaced with your internal SBS name, such as "SBS2008" and "office.example.com" should be replaced with the URL you use to gain access to the SBS from the Internet. Also, all lines beginning with [PS] are single lines - everything in bold is the one command and there are no spaces between the minus signs (-) and the property names immediately after them.
Next time anyone on the LAN opens Outlook and connects to your Exchange Server, the error message will not appear as we've configured the settings in Exchange Server correctly.
Update: Mark Wilton mentioned the following links to me also regarding this same issue:
A script to fix this issue from VirtualBarryMartin.me
Some PowerShell commands to fix the issue from Daniel Kenyon-Smith
Regards,
The Outspoken Wookie
Tick - The security certificate is from a trusted certifying authority.
Tick - The security certificate date is valid.
Cross - The name on the security certificate is invalid or does not match the name of the site.
If you press "Proceed", everything runs as normal. This is an annoying message that is caused by some improperly configured Exchange settings (normally caused by initially using a self-signed cert, then later replacing it with a purchased one), all of which are easily rectified after following KB940726, however below I've included the modified instructions for this to apply to an SBS installation.
In the following instructions, "CAS_Server_Name" should be replaced with your internal SBS name, such as "SBS2008" and "office.example.com" should be replaced with the URL you use to gain access to the SBS from the Internet. Also, all lines beginning with [PS] are single lines - everything in bold is the one command and there are no spaces between the minus signs (-) and the property names immediately after them.
- Start the Exchange Management Shell.
- To check the current settings of the ClientAccessServer property, enter the following command:
[PS] Get-ClientAccessServer | FL
If AutoDiscoverServiceInternalUri is not set to your external Uri (such as https://office.example.com/autodiscover/autodiscover.xml), then
- Modify the Autodiscover URL in the Service Connection Point. The Service Connection Point is stored in the Active Directory directory service. To modify this URL, enter the following command:
[PS] Set-ClientAccessServer -Identity "CAS_Server_Name" -AutodiscoverServiceInternalUri https://office.example.com/autodiscover/autodiscover.xml
- Modify the Autodiscover URL in the Service Connection Point. The Service Connection Point is stored in the Active Directory directory service. To modify this URL, enter the following command:
- To check the current setting of the WebServicesVirtualDirectory property, enter the following command:
[PS] Get-WebServicesVirtualDirectory
If the InternalUrl of EWS (SBS Web Applications) is not set to your external Uri (such as https://office.example.com/ews/exchange.asmx), then- Modify the InternalUrl attribute of the EWS. To do this, enter the following command:
[PS] Set-WebServicesVirtualDirectory -Identity "CAS_Server_Name\EWS (SBS Web Applications)" -InternalUrl https://office.example.com/ews/exchange.asmx
- Modify the InternalUrl attribute of the EWS. To do this, enter the following command:
- To check the current setting of the OABVirtualDirectory property, enter the following command:
[PS] Get-OABVirtualDirectory
If the InternalUrl is not set to your external Uri (such as https://office.example.com/oab), then
- Modify the InternalUrl attribute for Web-based Offline Address Book distribution. To do this, enter the following command:
[PS] Set-OABVirtualDirectory -Identity "CAS_Server_name\oab (SBS Web Applications)" -InternalUrl https://office.example.com/oab
- Modify the InternalUrl attribute for Web-based Offline Address Book distribution. To do this, enter the following command:
- To check the current setting of the UMVirtualDirectory property, enter the following command:
[PS] Get-UMVirtualDirectory
If the InternalUrl of UnifiedMessaging (SBS Web Applications) is not set to your external Uri (such as https://office.example.com/unifiedmessaging/service.asmx), then
- Modify the InternalUrl attribute of the UM Web service. To do this, enter the following command:
[PS] Set-UMVirtualDirectory -Identity "CAS_Server_Name\unifiedmessaging (SBS Web Applications)" -InternalUrl https://office.example.com/unifiedmessaging/service.asmx
Note This command is required only in an Exchange 2007 (SBS 2008) environment. This command no longer exists in an Exchange 2010 (SBS 2011) environment. Instead, the WebServices URL is used for this purpose.
- Modify the InternalUrl attribute of the UM Web service. To do this, enter the following command:
- Open IIS Manager, expand the local computer, and then in Application Pools, right-click MSExchangeAutodiscoverAppPool and click Recycle.
Next time anyone on the LAN opens Outlook and connects to your Exchange Server, the error message will not appear as we've configured the settings in Exchange Server correctly.
Update: Mark Wilton mentioned the following links to me also regarding this same issue:
A script to fix this issue from VirtualBarryMartin.me
Some PowerShell commands to fix the issue from Daniel Kenyon-Smith
Regards,
The Outspoken Wookie
Sega Follows CodeMasters, Acer and Sony
In what's clearly a case of "If it's good enough for them, then it's good enough for us", Sega have recently succumbed to a hacker attack obtaining their customers' personal data.
The Telegraph reported that whilst Sega is only reporting "Sega Pass is going through some improvements so is currently unavailable for new members to join or existing members to modify their details including resetting passwords" on their website, in an email sent to their customers, they admitted "We have identified that unauthorised entry was gained to our Sega Pass database."
The question I *have* to ask is: How many more high profile companies need to be hacked and have their confidential customer database details stolen before these susceptible companies start taking online/cloud security seriously? (Unfortunately, I feel the answer lies in the old "It won't happen to me" line of security principles - and this means that more and more people's confidential data will be stolen and made available to identity fraudsters.)
Regards,
The Outspoken Wookie
Sunday, June 12, 2011
Codemasters Follows Sony And Acer
Well, what seemed good enough for Sony (multiple times) and Acer now seems to have been good enough for Codemasters, a large British game developer. They have had their confidential client data breached, apparently everything but their credit card details...
Well, believe what you want, but it is just another example of how security is something that too many companies are not taking seriously enough.
Regards,
The Outspoken Wookie
Well, believe what you want, but it is just another example of how security is something that too many companies are not taking seriously enough.
Regards,
The Outspoken Wookie
Monday, June 06, 2011
Acer Exposes 40,000 Customer Records
Just as Sony seems to have gotten their vulnerabilities under control for a few weeks, Acer goes and gives away sensitive data from their customers.
It appears that an old username/password posted online to allow users to download a patch was used to gain access to not only over 40,000 customer accounts, but also Acer source code.
Oops!
Will these companies never learn that security is something that needs to be taken seriously? :(
Regards,
The Outspoken Wookie
Saturday, June 04, 2011
Human Dignity Campaigner Dr Jack Kevorkian Dies At 83
The well known campaigner for human dignity, Dr Jack Kevorkian, died on Friday 3 June, 2011 in Michigan, after being admitted to hospital suffering from kidney and respiratory problems. Dr Kevorkian had spent many years of his life dedicated to allowing humans to die with dignity when their death would otherwise be unavoidably painful and messy. He spent 8 years in a Michigan jail for these "crimes against humanity" as some have called this compassionate exercise.
I've always wondered why we can afford a level of dignity to our pets and other animals that we legislate against for humans - it makes no sense to me. Oregon seems to have seen the sense in allowing humans to die with some dignity and have, thanks to the efforts of Dr Kevorkian (and others), enacted the Death With Dignity Act which protects assisted suicide as a legitimate medical practice.
There's a difference between being alive and not being dead and maybe this is time to reflect on what this difference actually is, out of respect for the one man who brought this to the attention of the law makers.
Regards,
The Outspoken Wookie
Thursday, June 02, 2011
Today's Garden Addition
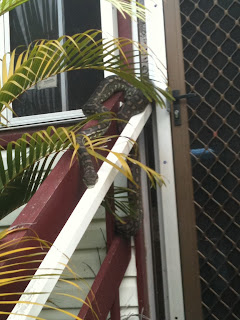
I heard the birds going nuts outside and "I know that noise"! :)
So, here's a few photos of today's snake! :)


Regards,
The Outspoken Wookie
So, here's a few photos of today's snake! :)

Yes, that's the first (little) rat I fed it. I had some rats left over from Cletus that are too large for my other snakes, so...

This gives you an idea of its girth - probably around 8cm in diameter.

Getting the entree down, and then I fed the larger rat (however it was eaten in a difficult place to photo, between stairs and palms.

Just looking at the flood light.
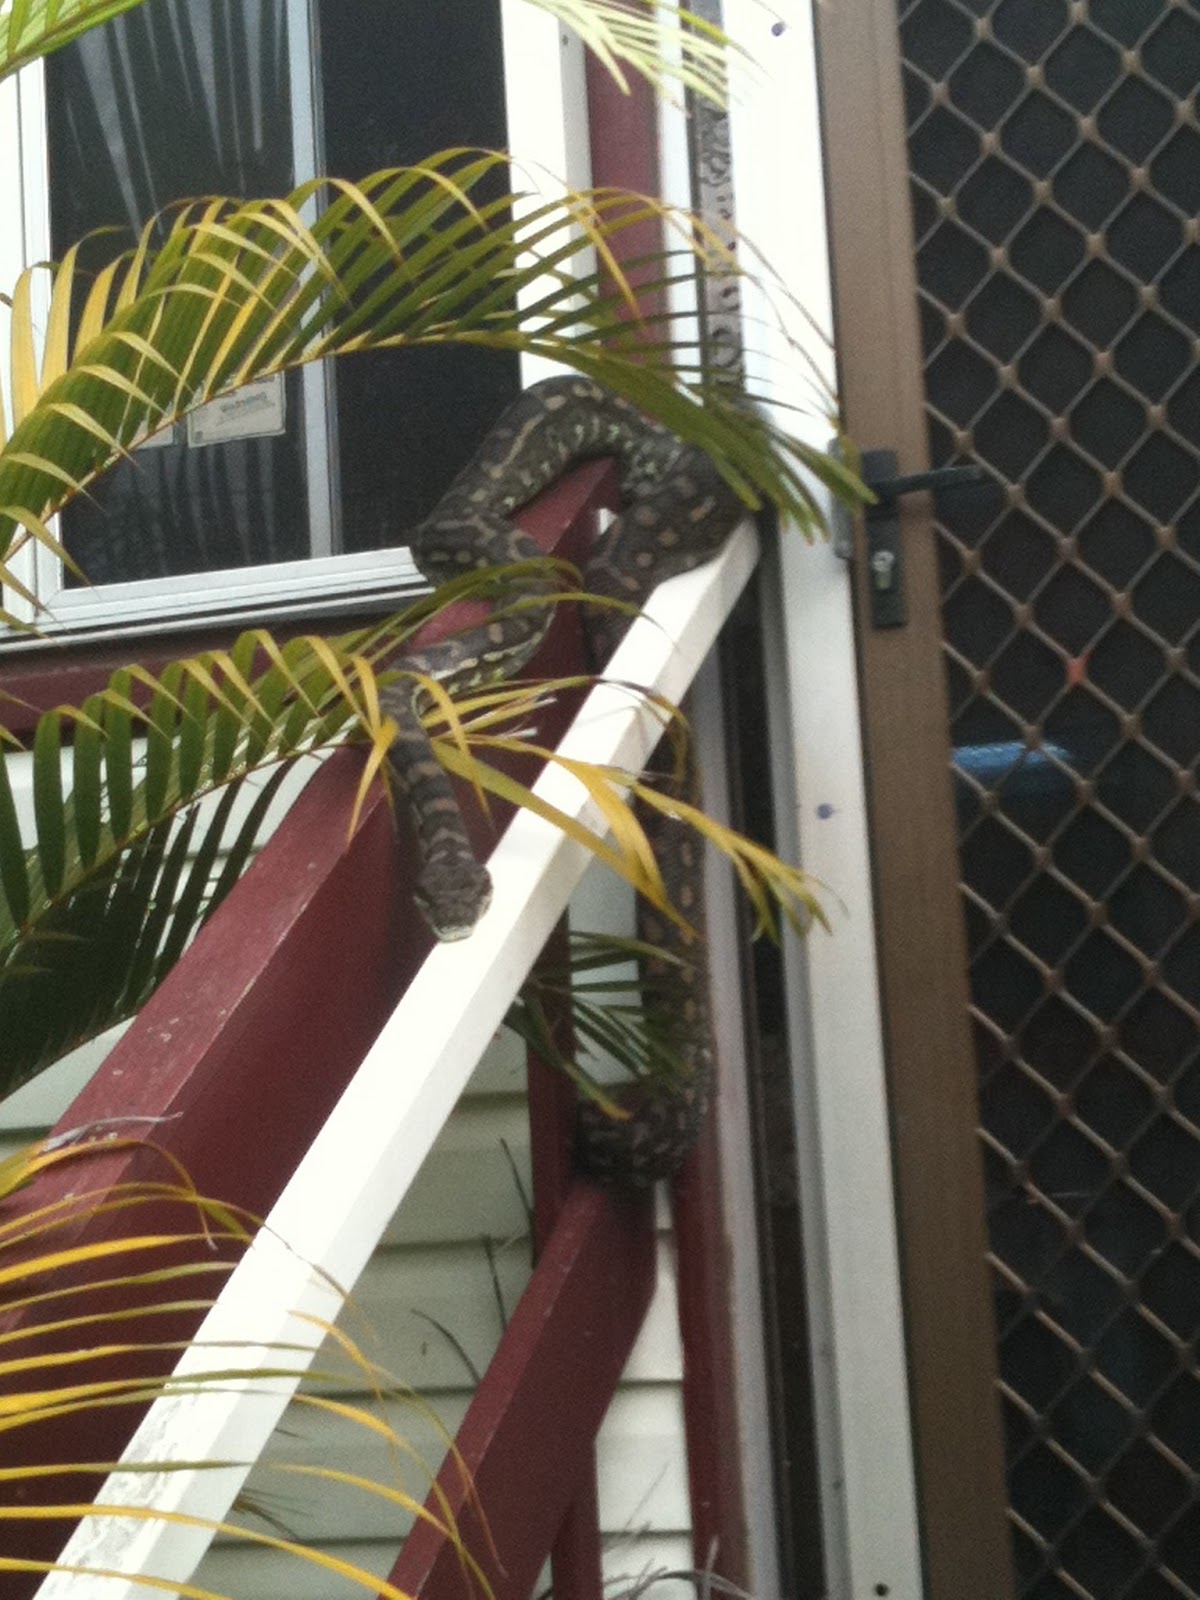
... and now looking at me. :)
Regards,
The Outspoken Wookie
Sunday, May 22, 2011
I Testify That The Rapture Did Occur
Friends, let me just say that I can attest to the fact that the Rapture did most definitely occur on May 21, 2011. All those people believing in the one, true supernatural god were taken up to heaven in a bright, warm, white light. Every single one who believed in the real god.
Unfortunately, that means that those of us who either a) believe in false gods or b) don't believe in any god are left here on Earth to live our lives as best we can. So that makes, at my best approximation, 7.1 billion people on the planet at around 17:55 on May 21 and 7.1 billion people on the planet at around 18:05 on May 21, 2011 - a total change of, well, a few more due to the net growth that occurred during that 10 minute period.
So, where does that leave people believing in whichever Mythical Sky Fairy they choose to believe in? In the same position as we Atheists - still here on Earth, waiting until we're all screwed. Except that the religious still choose to believe their particular creation myth instead of getting on with reality...
Regards,
The Outspoken Wookie
Saturday, May 21, 2011
Sony: The Caring Tech Company?
In my recent blog post (the 3rd about Sony's insecurity), I mentioned a recent vulnerability that was discovered in their website, close on the heels of over 100 million accounts becoming compromised. Any sane person would have thought that this, if nothing else, would have had Sony look at their web security worldwide.
Well, as reported at F-Secure, this is simply not the case.
How little does Sony truly care about their own insecurity, and therefore how much less do they seem to care about the security of your personal data that they store?
Regards,
The Outspoken Wookie
Well, as reported at F-Secure, this is simply not the case.
How little does Sony truly care about their own insecurity, and therefore how much less do they seem to care about the security of your personal data that they store?
Regards,
The Outspoken Wookie
Thursday, May 19, 2011
Sony and Insecurity Part III
I don't know if you can cast your mind back all the way to, well, my last blog post on May 3rd, 2011 when I reported on Sny's latest (at the time) pair of massive security blunders. In that I referred to a number of previous security issues that Sony had succumbed to (including one they actively perpetrated on their customers) and wondered if having over 100 million of their customers' accounts hacked would make them take security seriously.
Well, unfortunately, that doesn't seem to be the case. According to PC World, Sony's just taken their PSN login page down for maintenance to fix a recently discovered issue where anyone who has access to the information that they leaked (like a burst balloon) with their 100 million + account hack recently could easily reset the password of any legitimate PSN account holder. That in itself isn't good, but coming on the heels of one of the biggest technology-related security breaches we've seen, this is not just poor form, but more likely Sony clearly showing how much they actually care about their customers' data.
I'm quite disgusted that Sony cares so little for their customers that they haven't bothered putting more effort in now - especially now - to show that they are taking these issues seriously. If you also feel strongly about how Sony's treating your confidential information, I suggest contacting their CEO - the email I found for Howard Stringer is: howard_stringer@sonyusa.com
Regards,
The Outspoken Wookie
Tuesday, May 03, 2011
Sony and Insecurity Part II
Just when Sony thought it was safe to go and apologize for having 77 million PSN user accounts hacked into, they go and have another 24.6 million hacked via it's Sony Online Entertainment network. So that's over 100 million Sony users who have had personal data stolen.
Sony needs to make SERIOUS changes to the way they do business and the lessons they learn from this should also be lessons that other online service providers learn from. They are hard lessons to learn, sure, but they are essential lessons to learn.
Anyone using cloud solutions needs to know exactly how secure those services are - issues like this from Sony, a sizeable company, just show how susceptible we all are with these services.
Regards,
The Outspoken Wookie
Monday, May 02, 2011
Sony and Insecurity
Back in August 2007, I wrote this article on the Sony Rootkit V2 and then this clarification in early September, 2007. So, as you can see, Sony is no newcomer to misappropriating client data and mishandling personal data security.
Then they enforce region encoding on Blu-ray discs to ensure *their* important clients (aka movie studios) are protected from the general public.
Now they have had their entire Playstation Newtork hacked into and its personal data stolen - there's no way to know exactly what is stolen in a successful hack as hackers who know their trade know how to remove evidence of where they have been and what they have taken. Here's a good article on the security implications of this last Sony indiscretion.
How many more times will Sony breach the trust of its client base before people take a stand? Do people even know how sensitive the data is that they have stored in networks like the PSN and how easy it is to use this for identity theft? Somehow, I think this will pass silently in the night like most other serious security breaches have because no-one really understands how bad this sort of thing is. :(
Regards,
The Outspoken Wookie
Subscribe to:
Posts (Atom)