Thursday, June 02, 2011

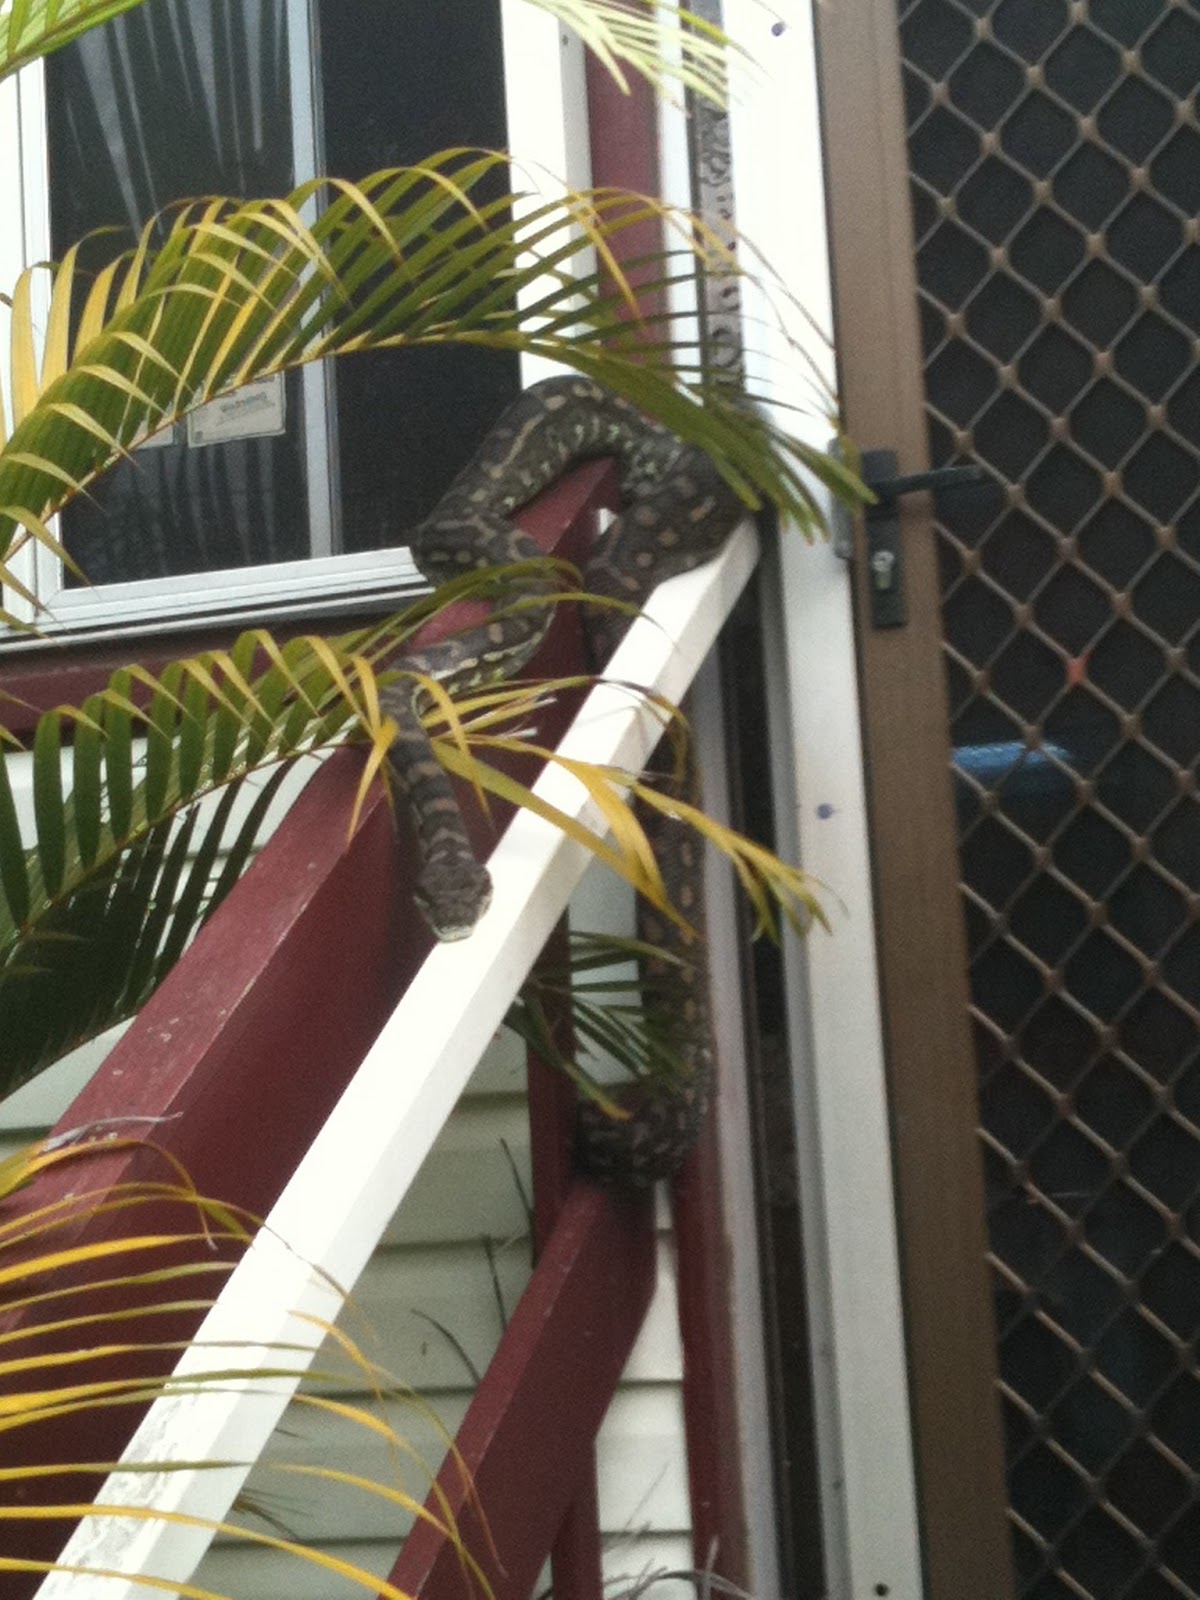
Today's Garden Addition

I heard the birds going nuts outside and "I know that noise"!  :)

So, here's a few photos of today's snake!  :)

Yes, that's the first (little) rat I fed it.  I had some rats left over from Cletus that are too large for my other snakes, so...


This gives you an idea of its girth - probably around 8cm in diameter.


Getting the entree down, and then I fed the larger rat (however it was eaten in a difficult place to photo, between stairs and palms.

Just looking at the flood light.

... and now looking at me.  :)


Regards,

The Outspoken Wookie

Sunday, May 22, 2011

I Testify That The Rapture Did Occur

Friends, let me just say that I can attest to the fact that the Rapture did most definitely occur on May 21, 2011.  All those people believing in the one, true supernatural god were taken up to heaven in a bright, warm, white light.  Every single one who believed in the real god.

Unfortunately, that means that those of us who either a) believe in false gods or b) don't believe in any god are left here on Earth to live our lives as best we can.  So that makes, at my best approximation, 7.1 billion people on the planet at around 17:55 on May 21 and 7.1 billion people on the planet at around 18:05 on May 21, 2011 - a total change of, well, a few more due to the net growth that occurred during that 10 minute period.

So, where does that leave people believing in whichever Mythical Sky Fairy they choose to believe in?  In the same position as we Atheists - still here on Earth, waiting until we're all screwed.  Except that the religious still choose to believe their particular creation myth instead of getting on with reality...


Regards,

The Outspoken Wookie

Saturday, May 21, 2011

Sony: The Caring Tech Company?

In my recent blog post (the 3rd about Sony's insecurity), I mentioned a recent vulnerability that was discovered in their website, close on the heels of over 100 million accounts becoming compromised.  Any sane person would have thought that this, if nothing else, would have had Sony look at their web security worldwide.

Well, as reported at F-Secure, this is simply not the case.

How little does Sony truly care about their own insecurity, and therefore how much less do they seem to care about the security of your personal data that they store?


Regards,

The Outspoken Wookie

Thursday, May 19, 2011

Sony and Insecurity Part III

I don't know if you can cast your mind back all the way to, well, my last blog post on May 3rd, 2011 when I reported on Sny's latest (at the time) pair of massive security blunders.  In that I referred to a number of previous security issues that Sony had succumbed to (including one they actively perpetrated on their customers) and wondered if having over 100 million of their customers' accounts hacked would make them take security seriously.

Well, unfortunately, that doesn't seem to be the case.  According to PC World, Sony's just taken their PSN login page down for maintenance to fix a recently discovered issue where anyone who has access to the information that they leaked (like a burst balloon) with their 100 million + account hack recently could easily reset the password of any legitimate PSN account holder.  That in itself isn't good, but coming on the heels of one of the biggest technology-related security breaches we've seen, this is not just poor form, but more likely Sony clearly showing how much they actually care about their customers' data.

I'm quite disgusted that Sony cares so little for their customers that they haven't bothered putting more effort in now - especially now - to show that they are taking these issues seriously.  If you also feel strongly about how Sony's treating your confidential information, I suggest contacting their CEO - the email I found for Howard Stringer is: howard_stringer@sonyusa.com


Regards,

The Outspoken Wookie

Tuesday, May 03, 2011

Sony and Insecurity Part II

Just when Sony thought it was safe to go and apologize for having 77 million PSN user accounts hacked into, they go and have another 24.6 million hacked via it's Sony Online Entertainment network.  So that's over 100 million Sony users who have had personal data stolen.

Sony needs to make SERIOUS changes to the way they do business and the lessons they learn from this should also be lessons that other online service providers learn from.  They are hard lessons to learn, sure, but they are essential lessons to learn.

Anyone using cloud solutions needs to know exactly how secure those services are - issues like this from Sony, a sizeable company, just show how susceptible we all are with these services.


Regards,

The Outspoken Wookie

Monday, May 02, 2011

Sony and Insecurity

Back in August 2007, I wrote this article on the Sony Rootkit V2 and then this clarification in early September, 2007.  So, as you can see, Sony is no newcomer to misappropriating client data and mishandling personal data security.

Then they enforce region encoding on Blu-ray discs to ensure *their* important clients (aka movie studios) are protected from the general public.

Now they have had their entire Playstation Newtork hacked into and its personal data stolen - there's no way to know exactly what is stolen in a successful hack as hackers who know their trade know how to remove evidence of where they have been and what they have taken.  Here's a good article on the security implications of this last Sony indiscretion.

How many more times will Sony breach the trust of its client base before people take a stand?  Do people even know how sensitive the data is that they have stored in networks like the PSN and how easy it is to use this for identity theft?  Somehow, I think this will pass silently in the night like most other serious security breaches have because no-one really understands how bad this sort of thing is.  :(


Regards,

The Outspoken Wookie

Sunday, April 24, 2011

Some Catholic Priests Can's See Molesting Boys As Wrong

Geoffrey Robinson, a retired Catholic Auxiliary Bishop from Sydney, says that some priests don't see the molestation of small boys as breaching their celibacy vows.  I say that regardless of the vows that they made to a religion based on a mythical sky fairy, anyone fiddling with a child is a filthy low-life scumbag that deserves to rot in jail for their offences.
Regards,

The Outspoken Wookie

Thursday, April 21, 2011

Happy Judgement Day

Today is Judgement Day.  All the best and I hope you, your family and friends survive.
Regards,

The Outspoken Wookie

Wednesday, April 20, 2011

Do journalists not spell check these days?

FFS, this is early childhood spelling, it's not even difficult!  (Sure, the death is tragic, but the spelling under the photograph is worse!)


(http://news.ninemsn.com.au/world/8239491/british-woman-dies-in-thailand-waterfall-tragedy)

Regards,

The Outspoken Wookie

Passwords v Passphrases v 2FA

Passwords suck.

Passphrases, on the other hand, suck less.

Two Factor Authentication (2FA) sucks the least.

Now, to give a bit more detail on this, passwords - a simple, usually less than 8-10 character word that someone uses to log into somewhere - are way, way too easily crackable and there are many "Top 100" or similar lists that have been published listing people's top password choices.  See this, this, and this to see just a few - possibly containg some of your passwords!  To see how the length and character set choice affect password "hackability", have a look at this page and also look at the calculator they offer - and 100,000 attempts/second isn't anything spectacular using modern computers.

So, if simple passwords suck, how do we address this properly?  Well, the best way is to forget you've ever heard the term "password" and automatically substitute "passphrase" where you read/see/hear this.  A passphrase is much more secure than a password because 1. It is longer, 2. It contains more character types than your average password (UPPER, lower, numbers, special characters (such as punctuation)), and 3. It is easier to remember (and often easier to type) than cryptic passwords that people think are secure.

A passphrase such as "On Thursday at 3:00 I put the cat out," or "After school finishes, I needa holiday!" are really easy to remember, will be typed faster than anything else you type after a short time, are very difficult to work out when shoulder surfing and have decryption times that make them unfeasible to crack before the information they protect becomes irrelevant.  They are even better for people who don't have cats or who aren't at school - yes, use a passphrase that's memorable, but not able to be directly associated with you.

Now, if you want even better security, combine the passphrase with some form of Two Factor Authentication.  This is where you need something to remember (the passphrase - the first factor) and something you have (a token, smartphone that receives a one-time code, or some software that talks back to a server and generates this one-time code - the second factor).  So, when you go to log in, you're prompted for your username and passphrase (as normal) and in addition to this, you're prompted for a one-time code that is generated, used, then discarded - the code is normally delivered on a key fob token or smartphone (app or SMS/text message).  This increases the security of your passphrase rather significantly - if someone manages to get your username and works out your passphrase, they also need to steal your key fob and/or smartphone to be able to log in.  That's what makes this a much more secure authentication method.

(Your "hole in the wall" card from your bank is a form of 2FA - you need your PIN (something you know) as well as the physical card to swipe (something you have) - one without the other isn't all that useful.

In the SMB world, functional 2FA basically means the RWW Guard and AuthAnvil products from http://www.scorpionsoft.com/ - and no this isn't a paid advert.  For that matter, Dana doesn't know I'm writing this blog entry and I don't think he even reads my blog.  I mention it here simply because it works and works well.

Also, as you should use a different passphrase for each different login, you may want to look at something like http://www.RoboForm.com/ to store these all in.  I've been using it for years now and find it a lot better than http://www.LastPass.com/, http://keepass.info/ or others, but whichever you choose, make sure it has a secure passphrase to protect it.

So, basically, forget passwords as they suck.  Use passphrases of decent length and complexity and you'll be orders of magnitude more secure.  If that's still not enough, combine this secure passphrase with some form of 2FA.  And remember - social engineering is still going to work in *way* too many cases.  Password crackers may have gotten a lot more sophisticated, but these massive password leaks prove that people's password choice sure hasn't!  :(


Regards,

The Outspoken Wookie

Tuesday, April 19, 2011

Blue LEDs in Baby Bredli Viv

I found some submersible aquarium LED lighting on eBay and thought that they'd work well not only for my aquariums, but also my snake vivs, so yesterday evening I made some mods to the smaller viv and this is how it turned out (using the blue LEDs for "moonlight" - the white ones are turned off for now):


It's an iPhone 3GS photo so it's not that great, but you can see the result!  I'm pretty happy with this.  I have these blue LEDs turned around so that they are a lot dimmer than they would be is facing into the main part of the viv, but I have the white ones (you can just see the top one up in the left of the viv) facing right into the viv - I'll use these when cleaning it out.

$10 each or so for these LED lights - and they do a damn fine job!  :)


Regards,

The Outspoken Wookie

Monday, April 18, 2011

Microsoft 1:0 Telstra

In what can only be an awesome move on Microsoft's part as far as increasing the sales of Office 365, can I just say *THANK FUCK*:

Office 365 Hits Public Beta, Small Businesses Get the Next Generation Cloud Productivity Service - but the *REALLY* awesome part of this is this:

Office 365 in Australia

In Australia, Microsoft Office 365 will be available via Microsoft Volume Licensing or through Telstra’s T-Suite service. (http://www.microsoft.com/en-au/office365/online-software.aspx)

That means that we, as resellers, should be able to source Office 365 through our normal disty channels and bypass Telstra totally.  WOO-FUCKING-HOO - this is a great day for all Microsoft partners who want to sell Office 365 but don't want to have to deal with the clusterfuck that is Telstra's T-Suite provisioning.  See this blog post for a bit more information on this issue and why I think this is such an excellent move on Microsoft's part.

Regards,

The Outspoken Wookie

Friday, April 08, 2011

More Baby Bredli Pics

OK, here's a couple of pics of my new baby Bredli just to give you a look at the cute little snakes.

I've not thought of names for them yet, but the first one's mum is Devine and the thing s/he's curled around is a regular cup hook:


And here's the second pic - this one's mum is Lizzie.  Again, s/he's curled around a cup hook.  The fake vine you can see there is 9mm in diameter...

At this point in time, they are about 6 weeks old.  :)


Regards,

The Outspoken Wookie

Wednesday, April 06, 2011

ShadowProtect Restore Issues

Thanks to Tony for bringing to my attention this blog post from Philip Elder regarding issues around restoring Windows F^HFista and WS2K8 images that were previously made using ShadowProtect.  This is also quite possibly an issue also with Win 7 and WS2K8R2 - I'm not 100% sure here, though the BCDEdit results do look similar to those in F^HVista and WS2K8, so I'd be placing money on this also being an issue

I'd suggest placing this script on the ShadowProtect IT USB key and running it on any F^HVista/WS2K8 (and Win 7/WS2K8R2) machine before taking an image.

StorageCraft is most likely working on a fix to this issue right now, especially considering Acronis' True Image has already addressed this.


Regards,

The Outspoken Wookie

Sunday, April 03, 2011

Baby Bredli

I bought a paid of Bredli hatchlings today.  Here's a photo of one, to give you an idea of the size...


Regards,

The Outspoken Wookie